

CSSLP試験,CSSLP試験問題集,CSSLP認定試験,CSSLP日本語試験|ktest
CSSLP試験概要
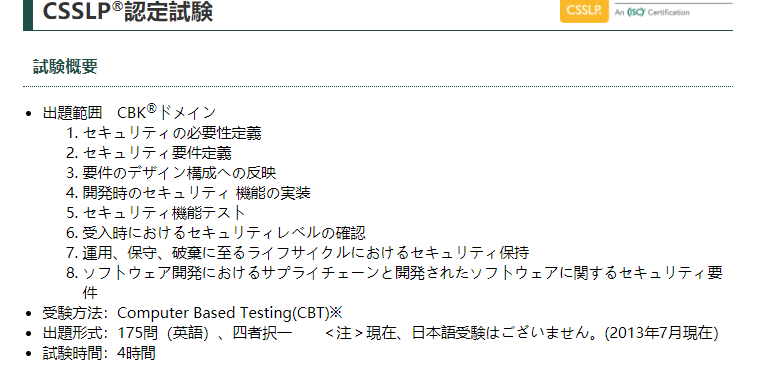
出題範囲 CBKドメイン
セキュリティの必要性定義
セキュリティ要件定義
要件のデザイン構成への反映
開発時のセキュリティ 機能の実装
セキュリティ機能テスト
受入時におけるセキュリティレベルの確認
運用、保守、破棄に至るライフサイクルにおけるセキュリティ保持
ソフトウェア開発におけるサプライチェーンと開発されたソフトウェアに関するセキュリティ要件
受験方法:Computer Based Testing(CBT)※
出題形式:175問(英語)、四者択一 <注>現在、日本語受験はございません。(2013年7月現在)
試験時間:4時間
Ktest問題集はIT専門家からすべての問題と解答を確認して、正解率が98%になります。(ISC)2 CSSLP Certification 資格CSSLP試験問題集は実験問題、多肢選択問題、単项の选択問題、ドラッグ アンド ドロップ問題及び穴埋め問題を提供しております。
人性化のサービス、よくお客様の立場から考えて、もっといいサービスを提供することはktestの信念です。 お客様が(ISC)2 CSSLP問題集を購入する前に無料で(ISC)2 CSSLP問題集のサンプルを試用することができます。(ISC)2 CSSLP試験問題は定期的にアップデートしています。
無料で365日以内に(ISC)2 CSSLP問題集の更新版を贈ります
ktestの(ISC)2 CSSLP試験問題集を買ったことがあるのはお客様に365日以内に無料で問題集の更新版を贈ります。お客様が持ってる問題集はきっと最新版でございます。
KtestはPDF版およびソフトウェア版を提供することができます。
ktest (ISC)2 CSSLP試験問題集のPDF版 はいつでも、携帯電話、コンピュータ、タブレットPCで勉強してもいいんです。どこ、いつでも勉強できます。
ソフト版は本格的な試験環境と同じです。受験者のために、本試験環境を適応することができます。受験の前に無料サンプルを体験して頂くことができます。
Ktestは無料でCSSLP Certification CSSLP試験問題集デモ(DEMO)を提供することができます。
Ktest試験問題集は真実の試験環境と同じです。お客様が購入する前に、無料でCSSLP(Certified Secure Software Lifecycle Professional)問題集のサンプルを使用してから、もっと自信を増やす。もし,弊社のCSSLP問題集を使ったら、試験に不合格だったら、ktestが全額で返金できます。ご安心ください。
ktestの新しいクラックされたCertifiedSecure Software Lifecycle Professional CSSLP試験の質問には、349のQ&Aが含まれています。 以下のISC認定CSSLP試験のデモの質問と回答を共有してください。
Which of the following individuals inspects whether the security policies, standards, guidelines, and procedures are efficiently performed in accordance with the company's stated security objectives?
A. Information system security professional
B. Data owner
C. Senior management
D. Information system auditor
Answer: D
Which of the following process areas does the SSE-CMM define in the 'Project and Organizational Practices' category? Each correct answer represents a complete solution. Choose all that apply.
A. Provide Ongoing Skills and Knowledge
B. Verify and Validate Security
C. Manage Project Risk
D. Improve Organization's System Engineering Process
Answer: ACD
The LeGrand Vulnerability-Oriented Risk Management method is based on vulnerability analysis and consists of four principle steps. Which of the following processes does the risk assessment step include? Each correct answer represents a part of the solution. Choose all that apply.
A. Remediation of a particular vulnerability
B. Cost-benefit examination of countermeasures
C. Identification of vulnerabilities
D. Assessment of attacks
Answer: BCD
You work as a Security Manager for Tech Perfect Inc. You have set up a SIEM server for the following purposes: Analyze the data from different log sources Correlate the events among the log entries Identify and prioritize significant events Initiate responses to events if required One of your log monitoring staff wants to know the features of SIEM product that will help them in these purposes. What features will you recommend? Each correct answer represents a complete solution. Choose all that apply.
A. Asset information storage and correlation
B. Transmission confidentiality protection
C. Incident tracking and reporting
D. Security knowledge base
E. Graphical user interface
Answer: ACDE
According to U.S. Department of Defense (DoD) Instruction 8500.2, there are eight Information Assurance (IA) areas, and the controls are referred to as IA controls. Which of the following are among the eight areas of IA defined by DoD? Each correct answer represents a complete solution. Choose all that apply.
A. VI Vulnerability and Incident Management
B. Information systems acquisition, development, and maintenance
C. DC Security Design & Configuration
D. EC Enclave and Computing Environment
Answer: ACD
 認証
 お支払方法
 お問い合わせ
 安全なお支払い


